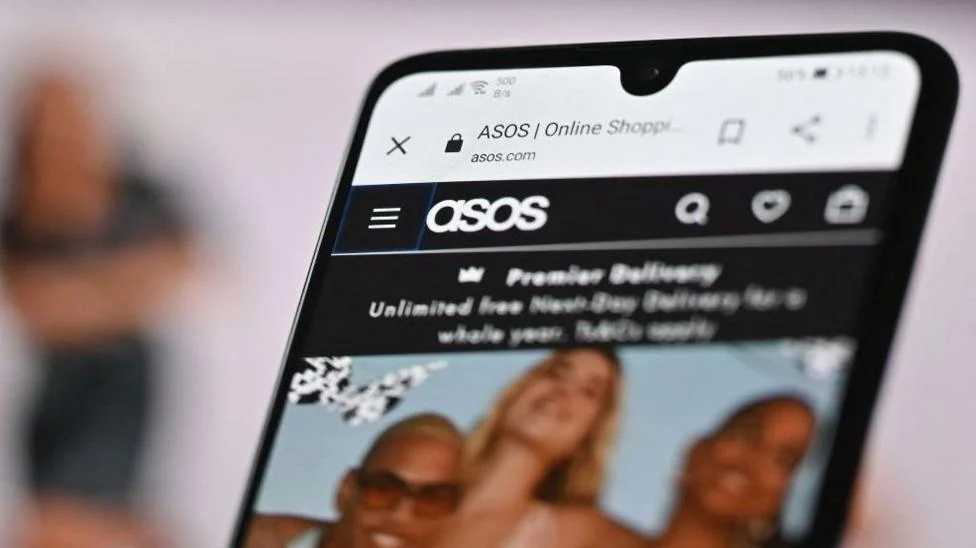

ASOS customers across the UK have reported receiving suspicious push notifications through the retailer’s mobile application. These alerts appear to be part of a ransom attempt aimed directly at the company’s internal IT and data protection teams, leaving many users confused as they appeared on their phone screens. According to dozens of people have, About receiving a strange message from the clothing and beauty store’s app, appearing on their phone screens. Whose tools are used by dozens of firms for collecting, analysing and storing data, this refers to the data storage company Snowflake. It is, however, very unusual for a data breach to be revealed quite so publicly – and for customers to be informed in this manner.
The message states, “Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.” The notification also includes a link directing users to a Telegram channel associated with a group identifying itself as the Xuanye Group, which reportedly created its channel on the same day the alerts began appearing.
Charlotte Wilson, head of enterprise at cyber-security firm Check Point, described the incident as a “deeply serious attack,” noting the brazen nature of turning a company’s own communication tool into a medium for extortion. She added that because users instinctively trust notifications from familiar applications, this breach poses a significant risk.
The message explicitly references Snowflake, a data storage platform utilized by various companies for analytics and storage. While it remains unconfirmed whether ASOS is a client of Snowflake or what specific data might be involved, Snowflake has been linked to several high-profile security incidents involving organizations like Ticketmaster and Santander in recent years.
Security experts emphasize that this method of disclosure is highly unconventional, as most cyber extortionists typically handle negotiations privately to secure a payout. Dan Bird of Horizon3 pointed out that the incident suggests a complex breach. Sending push notifications requires access to a company’s notification infrastructure, which is logically distinct from the Snowflake database mentioned in the hackers’ claim. With hackers hoping their discretion will result in a quiet pay-off, most extortions and negotiations by cyber criminals are conducted in private.
According to Bird, if both the claims of database access and notification system control are accurate, it implies that the attackers managed to obtain credentials that granted them entry into multiple internal systems. ASOS did not immediately respond to requests for comment regarding the situation. The Xuanye Group has maintained a minimal presence on its newly created Telegram channel, with only three posts currently visible, the latest of which concerns the ASOS incident.